Manufacturing is the most-attacked sector for the fifth year running and, frustratingly, most attempts still come through the same tried-and-tested avenues. Even though we know bad actors (now augmented by automation) are continually hunting for ecosystem weaknesses, legacy endpoints, outdated software, and fragmented oversight remain ongoing issues.
These persistent backdoors, amid increasingly automated attacks, threaten to make a bad security situation even worse.
Admins need to respond and fast. Now more than ever, network visibility across IT and OT is paramount to quickly catching threats before they spread. Funnily enough, the solution is rather unglamorous: disciplined, prioritized patching and proactive endpoint maintenance that closes the backdoors that attackers count on.
More Assets, Connections, and Backdoors
The numbers paint a concerning picture – manufacturing accounted for more than a quarter (27.7%) of total cybersecurity incidents last year. Beyond banking and financial services, which one might understandably think is the shortest path to people’s wallets, cybercriminals instead targeted the heavy machinery and often overlooked endpoints in manufacturing.
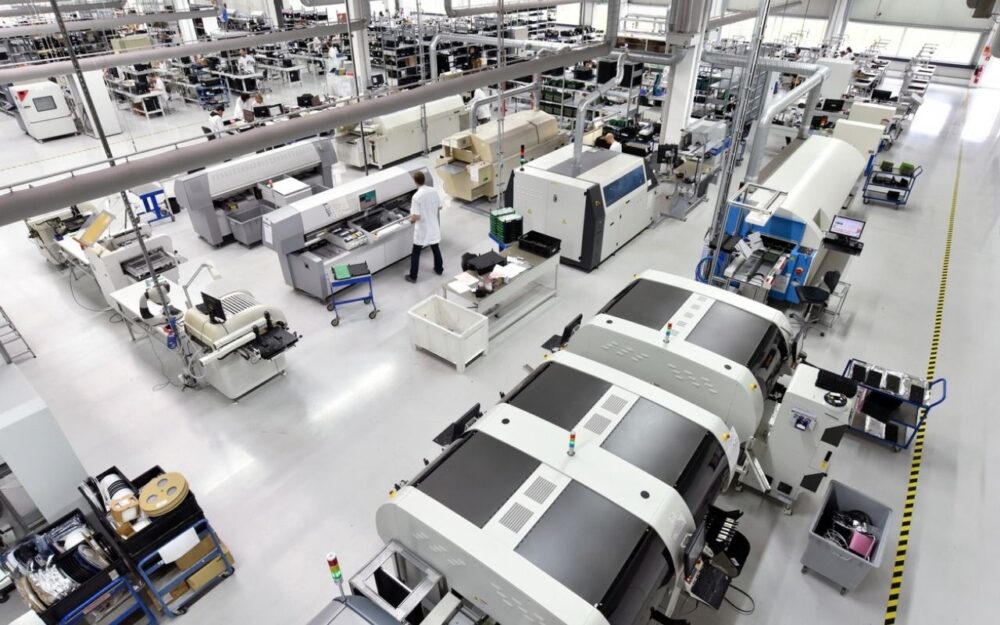
There are a few reasons why. First, the factory floor relies on multiple assets and interconnected supply chains. Breaking into an endpoint and shutting down the wider network can effectively hold up an entire production line for ransom – an expensive exercise since the world’s biggest 500 companies lose 11 percent of their annual revenue ($1.4 trillion) to unplanned production pauses.
Second, operational technology (OT) dominates this sector. Industrial computers like programmable logic controllers (PLCs) are common. These components, however, are typically less sophisticated than the information technology (IT) layer and therefore more vulnerable. Compound this with the fact that teams aren’t always trained or equipped to monitor both sides of the network (historically, heavy machinery didn’t connect to the wider network and was largely shielded from becoming a wider backdoor) and blind spots can occur.
Finally, Industry 4.0 introduces much more connectivity and greater exposure. One smart factory can encompass hundreds to thousands of devices – from networked floor sensors to ruggedized handheld scanners – which in turn require proper monitoring. This can be a challenge for patching, for example, since different devices require software updates at different times. Keeping a finger on the pulse of device and network health while tracking what’s updated becomes increasingly complicated across a large device ecosystem.

Read also this article
An Expensive Problem and Straightforward Solution
Despite the widespread and severe nature of this threat, the solution for manufacturing is rather straightforward. More threats demand stronger defenses, something the sector let slip in the preceding years of digital transformation. Even though attackers are getting smarter, defenders can keep them at bay with improved, if not somewhat boring, cyber hygiene practices.
Start with a holistic approach to device visibility. After all, you can’t defend what you can’t see, so connect your endpoints to a central console for at-a-glance visibility. This goes a long way toward providing better patching. By connecting to a unified endpoint management (UEM) platform, for example, admins can schedule software updates during off-peak hours.
Likewise, they can quickly see when endpoints drift out of compliance or run outdated software. Good patch management makes an immediate difference since bad actors more often target legacy devices and outdated software. In the past year alone, exploitation of public-facing software and system applications increased by 44%. We can and should move to nip this threat in the bud.
Also, go the extra mile to de-silo the signal. Networks can no longer operate separately between IT and OT. Instead, we need teams that are culturally and technologically aligned, understand one another, and can correlate across the environment. This way, empowered by anomaly detection at the managed-endpoint layer, teams can connect incidents and respond to them as quickly as possible.
Remember, redoubling defenses in manufacturing is as much about improving security as it is about protecting uptime. The latter is the lifeblood of this sector and leaders should keep in mind that fewer successful attacks effectively translate to better productivity. Ideally, with the sector squarely in hackers’ crosshairs, this should be reason enough to strengthen the network posture and take the target off of manufacturing’s back.
Read also this article
The Future of Fighting Automation With Automation
Of course, in addition to perfecting the defensive basics, there’s also something to be said for how automation can assist network defenders rather than just attackers. The pace of change is accelerating and it will only become harder for admins to remediate threats manually while the other half of the ledger increasingly operates autonomously. The answer is safely onboarding smart solutions that can run their own root-cause checks, catch endpoints that have fallen behind on patches, and apply routine fixes.
Endpoint management vendors, mine included, are starting to build this through agents that work within pre-defined guardrails. Routine fixes happen automatically, so a known vulnerability doesn’t sit open while a technician works through a ticket queue. More consequential actions (like wiping a device, isolating an endpoint, or changing privileged access) still go to a person for approval.
None of this displaces the fundamentals discussed above but instead scales them. Done right, governed autonomous defenses help stretched teams keep pace with visibility and patch hygiene at the scale modern manufacturing runs without adding headcount.
Teams can’t and won’t keep up if the attack surface keeps growing at its current rate. As a result, if we don’t act, manufacturing will likely remain the top target for hackers. The sector needs to respond in kind and close the known gaps. In practice, this doesn’t require anything extraordinary, just a concerted effort to improve overall cyber hygiene, unite IT and OT, and let automation (safely) take some of the device management load. If we can do that, the factory floor stops being the easy way in.